Teknosfera Newsroom
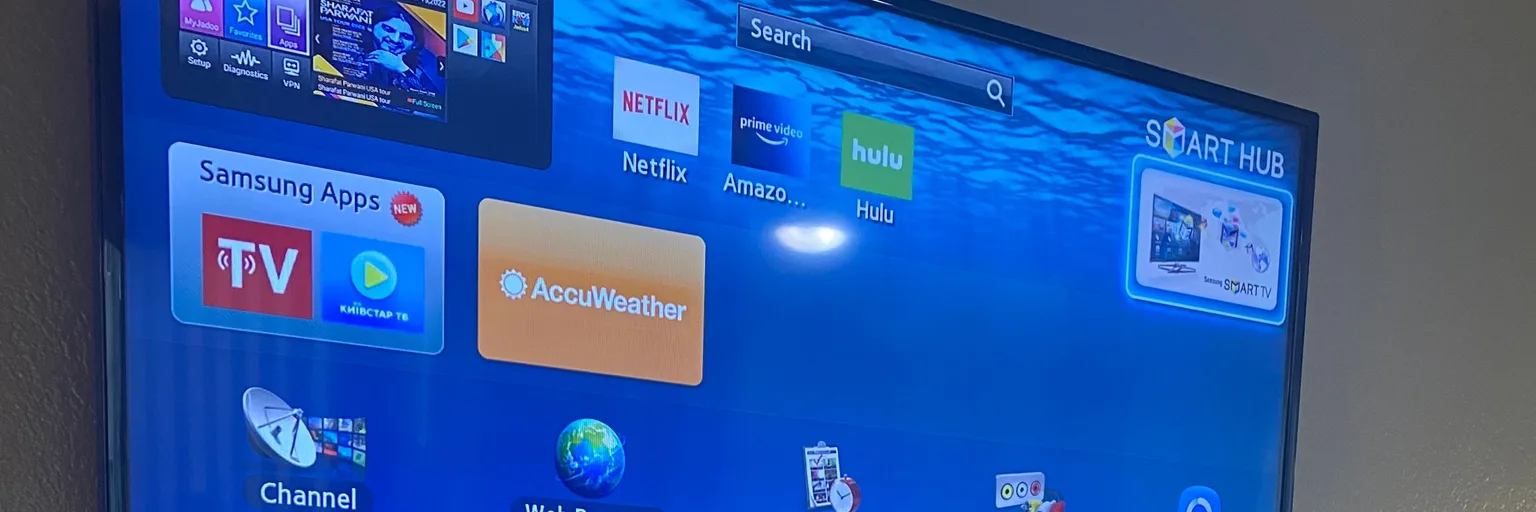
A root shell on a Samsung TV proves your living room is an unpatched PC
Smart TVs are long-lived networked Linux computers, and the root exploits piling up show why vendors should owe TV owners phone-style update promises.
Smart TVs are long-lived networked Linux computers, and the root exploits piling up show why vendors should owe TV owners phone-style update promises.
A breach of 11,774,247 CAPCOM ID records is not "just emails". Publishers that run account systems at this scale should answer to the standards of any consumer platform.
The flaw hitting Node.js and, reportedly, Python sits in a Brotli decoder, not in HTTP/2. That makes it a lesson about shared code nobody audits, and about patching as emergency work.
Bitcoin Core will now patch and disclose easily rediscoverable bugs fast, because the old embargo logic assumed bugs were hard to find, and AI is ending that assumption.
A public iPhone hacking demo and a fresh zero-day patch show Apple's security reputation is earned through constant attack and fast fixes, not through any promise of invulnerability.
Locking out unvetted AI agents is defensible while identity, consent and liability rules are missing, but banks must build a sanctioned access path instead of fortresses.
Mythos-style AI made vulnerability discovery abundant. The real bill is the human labor of fixing what it finds, and banks are the first to receive it.
The ConnectWise Cloud Backup attack shows that one vendor credential plus an agentic AI tool can reach hundreds of tenants. Backup and MSP tools now belong in tier zero.
Two AI-found PHP flaws pushed governments and major sites offline. The real lesson is that discovery now outpaces patching, and the gap is where defenders lose.
The eMudhra compromise shows that HTTPS can remain exposed outside the browser, where revocation is uneven, trust stores lag, and users have little chance to see the difference.
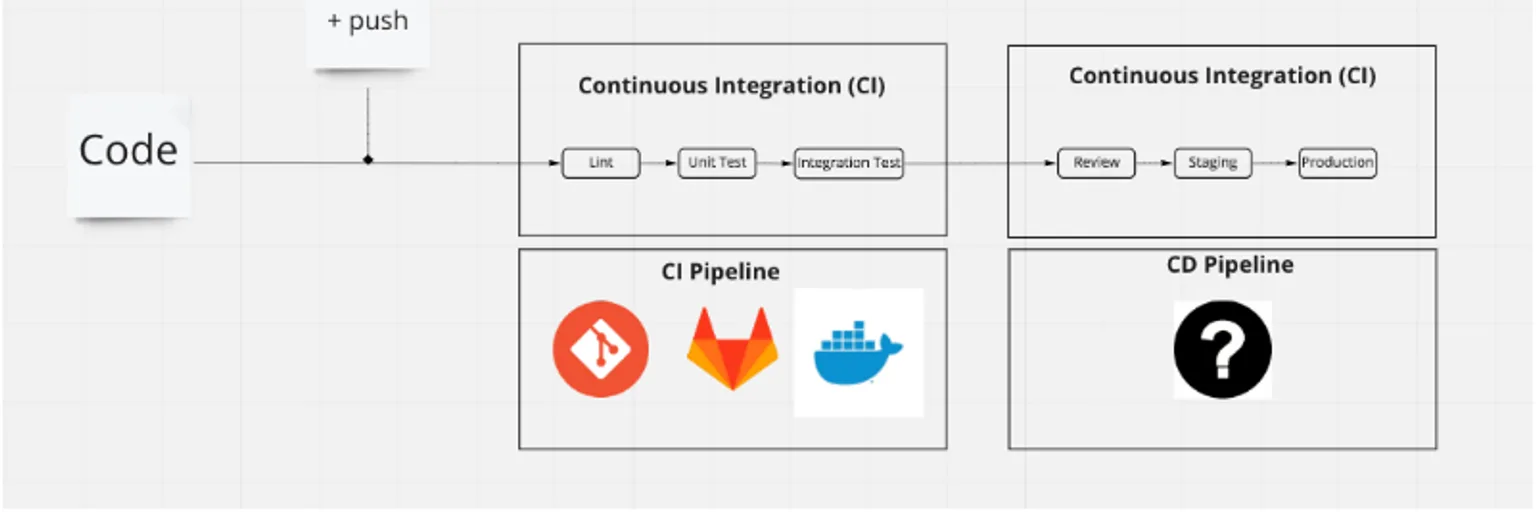
A critical GitLab vulnerability is a reminder that developer infrastructure can become a supply-chain attack path, not merely a collaboration tool to patch later.
HTTP/3 brings faster connections and multiplexing, but QPACK attacks show that protocol complexity can turn performance features into expensive failure modes.
Two leaked critical PHP flaws are a warning that patching is only half the problem when websites depend on aging hosting, plugins and unmanaged servers.
Zoom’s real-time warning is a useful safety layer, but identity in video calls now requires authentication, provenance and human checks—not just convincing pixels.
The recent Ticketmaster Brazil data breach reminds us that massive data hoards, especially those relying on third parties, create irresistible targets for cybercriminals, putting user trust and privacy at stake.
Hornetsecurity's enhanced suite for Microsoft 365 highlights a crucial truth: comprehensive cloud security in an AI-driven world demands robust third-party solutions to fill the gaps left by native offerings.
The recent arrest of an 18-year-old swatter, despite VPN usage, starkly demonstrates that a single layer of obfuscation isn't enough to hide your true identity online, as connected personal data often remains exposed.
Google's latest AI integrations in Android move beyond simple threat blocking, offering sophisticated, context-aware protection that actively intercepts evolving mobile fraud and phishing tactics.
The surge in unauthorized AI tool usage by employees isn't just a productivity hack; it's a silent crisis exposing corporate data and challenging traditional governance models.
Pyongyang's latest underwater weapon test signals a dangerous new era where artificial intelligence empowers less technologically advanced states, challenging global stability.